Dapr Sentry control plane service overview
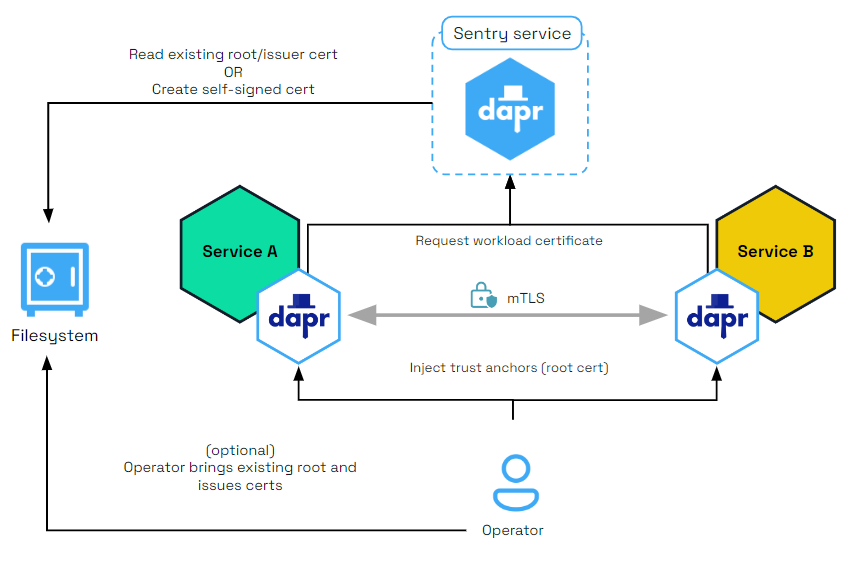
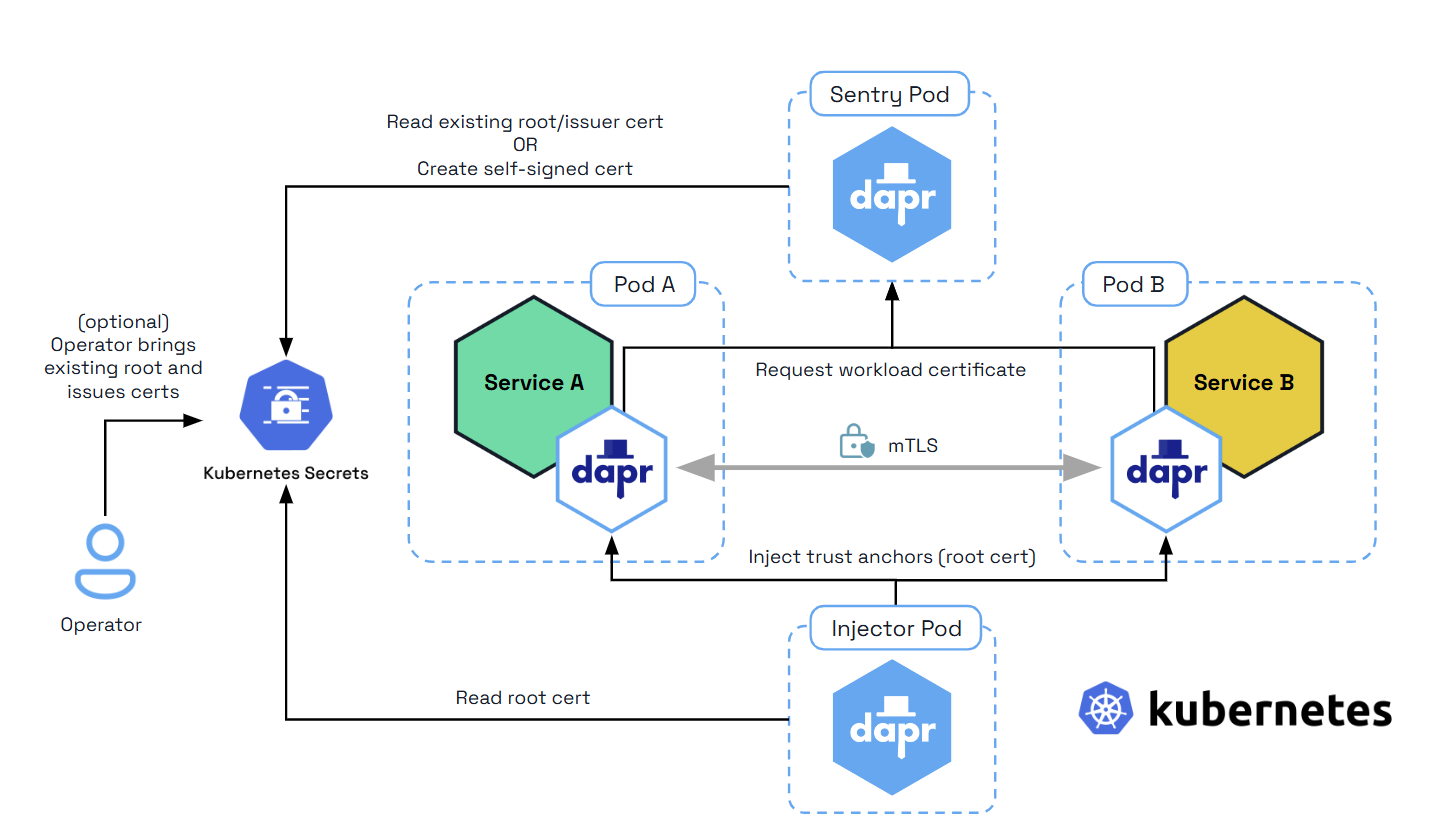
The Dapr Sentry service manages mTLS between services and acts as a certificate authority. It generates mTLS certificates and distributes them to any running sidecars. This allows sidecars to communicate with encrypted, mTLS traffic. For more information read the sidecar-to-sidecar communication overview.
On Kubernetes, Sentry also stamps the requesting pod’s container image references into each issued workload certificate as a custom X.509 extension, giving downstream systems verifiable supply-chain provenance of the software behind each workload identity.
Self-hosted mode
The Sentry service Docker container is not started automatically as part of dapr init. However it can be executed manually by following the instructions for setting up mutual TLS.
It can also be run manually as a process if you are running in slim-init mode.
Kubernetes mode
The sentry service is deployed as part of dapr init -k, or via the Dapr Helm charts. For more information on running Dapr on Kubernetes, visit the Kubernetes hosting page.
Additional sentry container arguments
Use the dapr_sentry.extraArgs Helm value to pass extra command-line arguments to the sentry container. Use this value for sentry flags that have no dedicated Helm value. The value is a list of strings. It defaults to []. Dapr appends each argument after the built-in sentry container arguments.
dapr_sentry:
  extraArgs:
    - "--jwt-ttl=48h"
    - "--healthz-listen-address=127.0.0.1"
--healthz-listen-address sets the address the sentry healthz server listens on, and --metrics-listen-address sets the address of its metrics server. Both default to all interfaces.